Why it matters that your IT provider is CMMC Level 2 certified

Mike Adcock
Why CMMC Level 2 certification matters: a summary
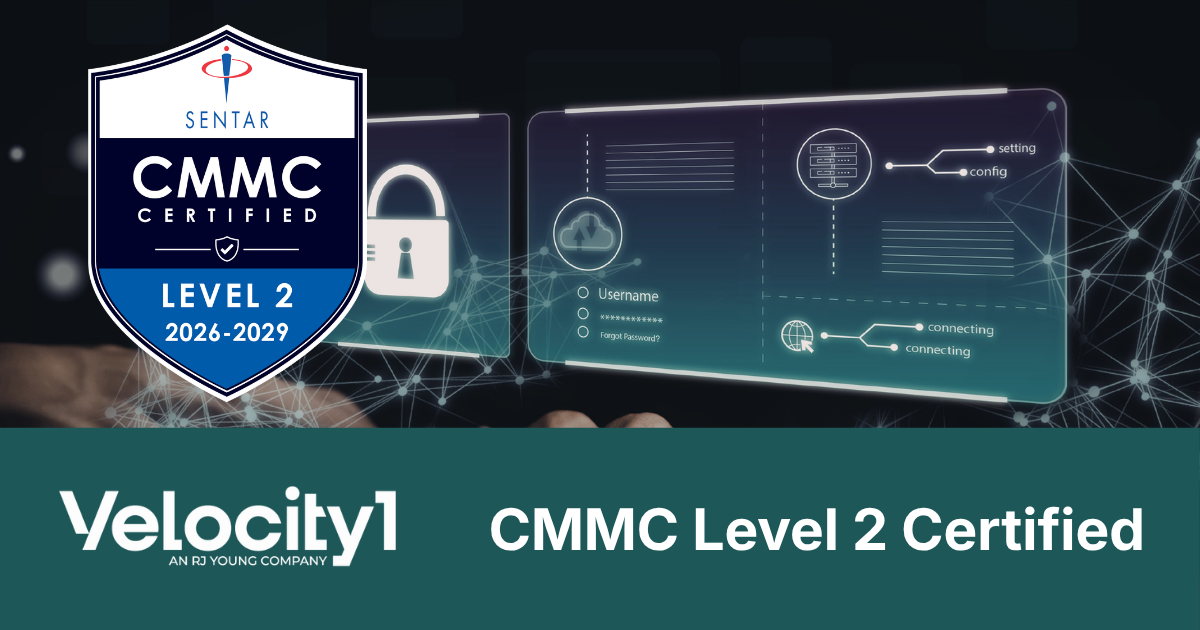
If you do defense work, your managed IT provider is already part of your compliance picture. The team that manages your endpoints, network, and security tools also manages the systems that hold your Controlled Unclassified Information (CUI). That's why it’s important that Velocity1 now holds Cybersecurity Maturity Model Certification (CMMC) Level 2 certification, confirmed by Sentar, an authorized Certified Third-Party Assessment Organization (C3PAO), on September 15, 2026.
Here's what a CMMC Level 2 certification means for businesses that do defense work:
- Security is a key element of how you operate. If you handle CUI, you're required to protect it, and so are the providers whose services touch that data. This certification means an independent assessor has confirmed your provider meets that standard.
- On July 13, 2026, the Department of War suspended CMMC Phase II, which would have added third-party assessment requirements to defense contracts, while it conducts a reform review. Velocity1 chose to complete its Level 2 certification anyway, to demonstrate our commitment to protecting sensitive data.
What CMMC Level 2 certification is
The CMMC program sets cybersecurity requirements for companies in the Defense Industrial Base (DIB), including the contractors, subcontractors, and suppliers that support Department of War (DoW) programs (the department is also still known as the Department of Defense). A CMMC Level 2 certification, issued after a C3PAO assessment, is independent verification that an organization meets the DoW's requirements for protecting CUI.
CMMC has three levels. Level 1 covers basic safeguarding of Federal Contract Information, which is information provided by or created for the government under a contract that isn't intended for public release. Level 2 applies to organizations that handle CUI, such as technical drawings, specifications, and other sensitive but unclassified program data. Level 3 applies to CUI tied to the DoW's highest-priority programs. It requires a Level 2 C3PAO certification first, plus 24 additional requirements from NIST SP 800-172, and the assessment is performed by the Defense Industrial Base Cybersecurity Assessment Center (DIBCAC) rather than a C3PAO.
Level 2 maps to the 110 security requirements in Revision 2 of NIST SP 800-171, a standard from the National Institute of Standards and Technology (NIST) for protecting CUI when it's stored, processed, or transmitted on non-federal systems and networks. Its requirement areas include access control, incident response, configuration management, and audit and accountability. An organization can self-assess against these requirements or be assessed by a C3PAO. The contracts it pursues set the minimum: some require only a self-assessment, while others require a C3PAO assessment. In a C3PAO assessment, an accredited assessor reviews your documentation, interviews your team, and tests whether your controls work in practice.
Velocity1’s assessment was conducted by Sentar, an authorized C3PAO that works across the national security sector. Reaching CMMC Level 2 reflects a serious commitment to safeguarding sensitive information and building operational resilience, and Sentar's independent assessment gives Velocity1 a solid foundation for meeting DoW cybersecurity requirements.
Why your managed IT provider is part of your CMMC compliance strategy
If your IT provider's services touch your CUI environment, those services fall within the scope of your assessment. Your System Security Plan (SSP) must document the provider and the services it provides.
Under CMMC rules, a provider that manages IT or security services on your behalf is considered an external service provider (ESP) when your CUI or Security Protection Data, such as log or configuration data, is processed, stored, or transmitted on its assets. A typical managed IT provider administers user accounts, patches servers, monitors endpoints, manages firewalls, and runs security tools. All of those activities involve the systems and security controls your assessment will examine.
When an assessor evaluates your organization, they'll want to know how your managed IT provider handles access, logging, change management, and incident response. This is true whether you rely on fully managed IT services or a co-managed model. Either way, the provider's security practices become part of your compliance story.
What a CMMC certified MSP changes for your business
A CMMC certified MSP gives your business three advantages: a key provider whose own environment has already been independently verified, guidance based on experience, and a partner whose daily operations already meet rigorous security standards.
1. Your provider has already been assessed. When your managed IT provider holds CMMC Level 2 certification in its own right, it means that one of the biggest dependencies in your environment has already been examined by a qualified third party. That doesn't replace your own assessment, and the provider's services remain within your assessment scope, but it gives your assessor independent evidence about the provider's own security practices.
2. You receive guidance based on experience. Velocity1 has walked assessors through our environment and answered detailed questions about it. That experience shapes how we assist clients, from scoping the CUI environment to documenting how controls operate.
3. Security is built into daily operations. To pass CMMC Level 2 certification, security has to be built into how a provider operates across its in-scope environment. The certification means an independent assessor has confirmed that is the case. For clients, that discipline carries into every ticket, patch cycle, and access change your provider handles for you.
Questions to ask before choosing managed IT services for defense contractors
If you're evaluating managed IT services for a defense contractor, ask providers these questions:
- Do you hold CMMC Level 2 certification yourselves? If so, who conducted the assessment?
- Which NIST SP 800-171 controls will you be responsible for in our environment?
- Can you provide documentation of your own controls for our assessment?
- Have you supported clients through a C3PAO assessment or a self-assessment?
- How do you handle access to our systems, and how is that access logged and reviewed?
CMMC Level 2 FAQs for defense contractors
Does my MSP need to be CMMC certified? Under the current rules, a managed service provider isn't required to hold its own certification. Instead, the services it provides fall within the scope of your assessment. However, a provider with its own CMMC Level 2 certification gives you independent evidence to point to. The DoW's CMMC Reform Task Force is reviewing the program, and its recommendations haven't been released yet, so watch for updates that could change how providers are treated.
Is CMMC still required after the Phase 2 pause? Yes, in part. CMMC Phase 1 self-assessment requirements remain in effect, and DFARS 252.204-7012 still requires contractors to protect CUI using NIST SP 800-171. What's on hold is Phase 2, which would have required third-party assessments in DoW contracts. Under the suspension, existing third-party assessment requirements are being removed from solicitations and contracts.
What is an external service provider (ESP)? An ESP is an outside organization that provides IT or cybersecurity services on your behalf and processes, stores, or transmits your CUI or Security Protection Data (such as log or configuration data) on its own assets. Managed IT providers and managed security providers are common examples.
How long does CMMC Level 2 certification last? A Level 2 certification from a C3PAO assessment is valid for three years, provided the organization submits an annual affirmation of continued compliance.
Managed IT services from a CMMC Level 2 certified provider
Velocity1 supports organizations in and alongside the defense industrial base, whether you need fully managed IT support or a co-managed partner that extends your in-house team. We have first-hand CMMC Level 2 experience, which expands what we bring to our clients. Companies getting ready for their own CMMC assessments can now work with a team that has been through the process firsthand, rather than one that only knows the requirements in theory. Managed IT clients gain an advantage in their own assessments: they can show that their ESP holds its own CMMC Level 2 certification, verified by an independent assessor. Going forward, Velocity1 will build the certification into our work with clients and prospects in and around the defense industrial base: in practice, this will include providing continuous monitoring, log review, remediation, patch management, and Plan of Action and Milestones (POA&M) support after CMMC prep and assessment.
If CMMC is on your roadmap, or you're wondering how your current IT provider would fare under an assessment, let's talk. Contact Velocity1 to schedule a conversation with our team.